Fine-grained, column-level access control with a plain-English preview of exactly what a rule does before you save it — covering the Lakehouse, AI Studio, AI Factory and Data Catalog from a single policy engine.
Row, column and table-level rules over structured catalog data, with Allow Conditions, Deny Conditions and a separate Row Level Filter tab for record-level predicates.
Equivalent rules scoped to the vector and embedding collections used by AI Studio agents and AI Factory-served models — so RAG obeys the same rules as SQL.
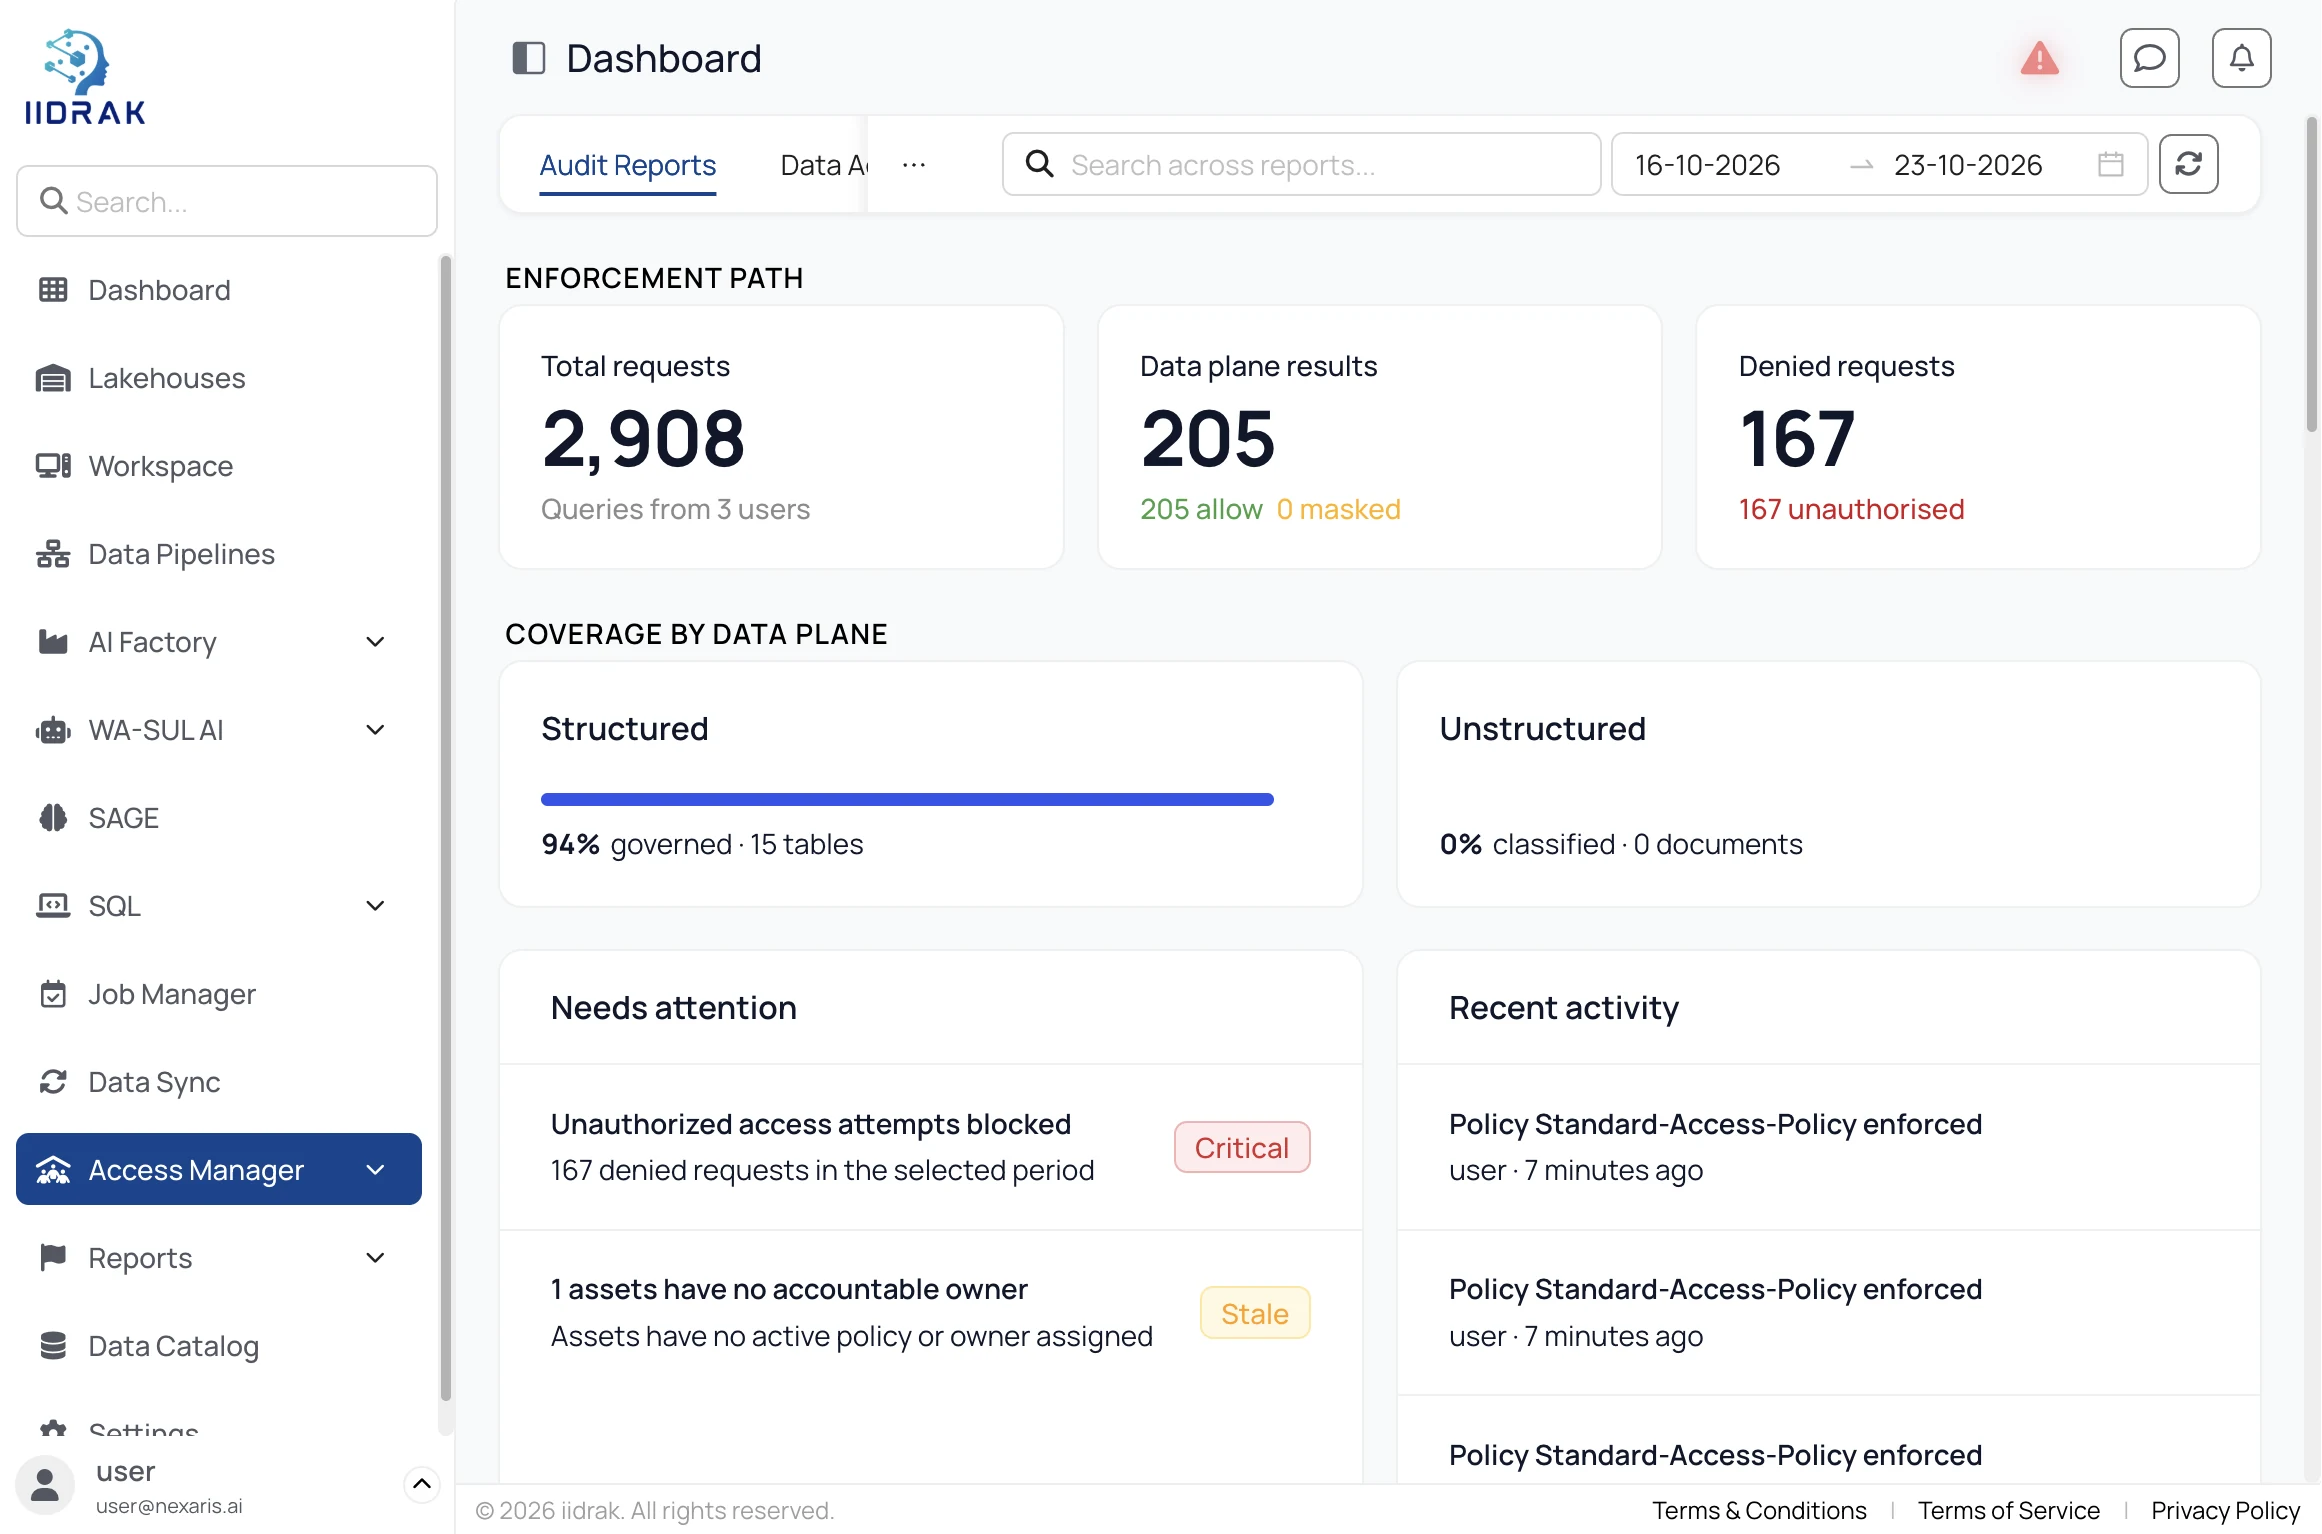
Total requests evaluated, data-plane results split into allowed versus masked, denied requests, and the percentage of structured tables and unstructured documents actually governed.
Build a rule and watch it render as a sentence: "User dev has read access to columns branch_id, branch_code, branch_name from the branches table in the banking catalog." It is generated from the same values used to enforce the policy, so if the sentence is wrong, the rule is wrong.
A query returning fewer columns than the table holds is column-level masking working as intended — the user still gets an answer, scoped to what they are cleared to see.
The coverage panel surfaces assets with no policy at all, so compliance readiness becomes a punch list rather than an audit surprise.
Because Nexaris federates data in place rather than copying it, there are no new data stores to secure, no egress paths to monitor and no additional data at rest to encrypt.
Guardiuum has nothing to enforce policy over on its own, so it deploys alongside at least one of the other four products — and appears in every deployment pattern.